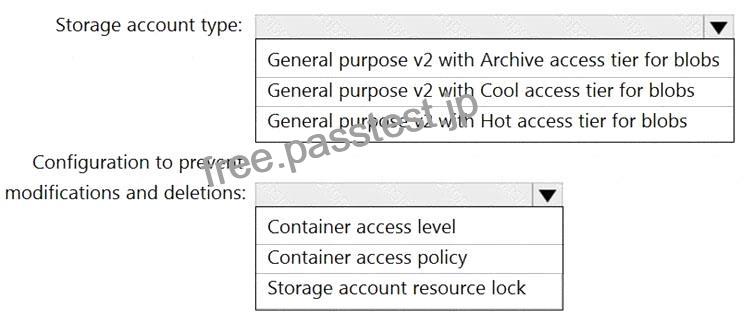
質問108、 機密データ用のAzureStorageソリューションを計画しています
a。データは毎日アクセスされます。データセットは10GB未満です。
次の要件を満たすストレージソリューションを推奨する必要があります。
*ストレージに書き込まれるすべてのデータは5年間保持する必要があります。
※一度データを書き込むと、データの読み取りのみが可能になります。変更や削除は防止する必要があります。
* 5年後、データは削除できますが、変更することはできません。
*データアクセス料金を最小限に抑える必要があります
あなたは何をお勧めしますか?回答するには、回答領域で適切なオプションを選択します。
注:正しい選択はそれぞれ1ポイントの価値があります。
Explanation
Graphical user interface, text, application Description automatically generated
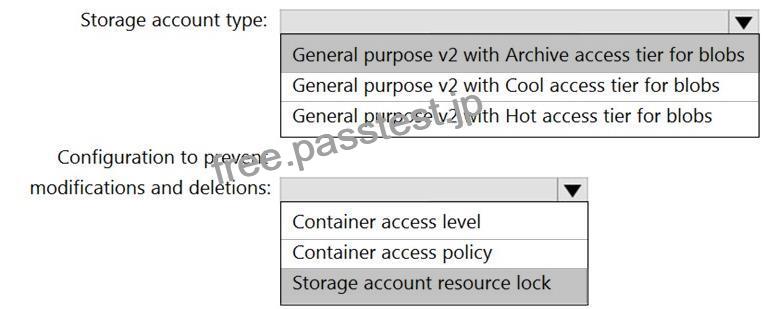
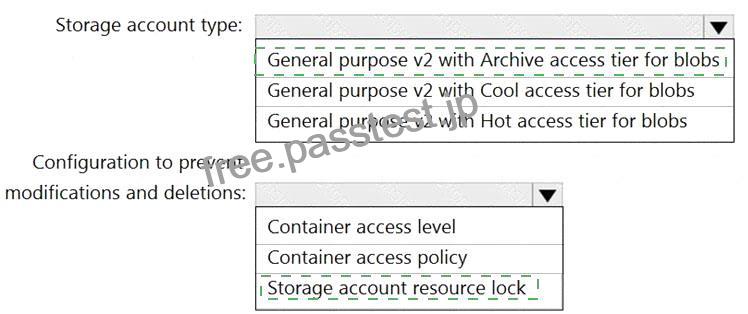
Box 1: General purpose v2 with Archive acce3ss tier for blobs
Archive – Optimized for storing data that is rarely accessed and stored for at least 180 days with flexible latency requirements, on the order of hours.
Cool – Optimized for storing data that is infrequently accessed and stored for at least 30 days.
Hot – Optimized for storing data that is accessed frequently.
Box 2: Storage account resource lock
As an administrator, you can lock a subscription, resource group, or resource to prevent other users in your organization from accidentally deleting or modifying critical resources. The lock overrides any permissions the user might have.
Note: You can set the lock level to CanNotDelete or ReadOnly. In the portal, the locks are called Delete and Read-only respectively.
* CanNotDelete means authorized users can still read and modify a resource, but they can’t delete the resource.
* ReadOnly means authorized users can read a resource, but they can’t delete or update the resource.
Applying this lock is similar to restricting all authorized users to the permissions granted by the Reader role.
Reference:
https://docs.microsoft.com/en-us/azure/storage/blobs/storage-blob-storage-tiers